Delegation Receipt Protocol v2.1.0

The user signs.
The operator cannot
widen scope after.

Authproof gives every agent action a cryptographic receipt that existed before execution started. Not reconstructed from logs. Not the operator's word against yours. Proof you can check after the fact. An audit and attribution layer for honest deployments: it proves what the user authorized before the agent acted. It does not stop a dishonest operator from refusing to run the gate.

install
# JavaScript
npm install authproof

# Python
pip install authproof-py

Want managed infrastructure? cloud.authproof.dev — free tier available.

Read the white paper →

01 / operator claims

The operator claims you authorized it.

Right now there is no cryptographic record of what you actually told your agent to do. The company running it can say anything.

02 / model substitution

The model was swapped after you signed.

An operator can substitute a modified model after authorization. Model-state attestation (an optional gate check) detects the drift and blocks the action, and the mismatch is recorded in the audit log.

03 / server-side logs

The audit trail is server-side logs.

Logs can be written after the incident. A Delegation Receipt exists before the first action. That is not the same thing.

04 / confidential deployment

Confidential Deployment

Bind receipts to enclave measurements on TDX and Nitro hosts. The measurements are software-computed and self-attested by default, not hardware-signed quotes. Real hardware guarantees require real TEE hardware.

05 / session state

Session State

Adaptive risk-aware authorization. Trust decay, sensitivity classification, real-time threat scoring.

06 / approval outcome logging

Approval Outcome Logging

Noise vs signal scoring. Threshold recalibration. Approval fatigue detection.

Two primitives. One complete chain.

Thirteen verification checks (slots 1–11, 14, 15). Every one must pass before execution proceeds. Scope defined from observed behavior, not guesswork.

authproof-cli
$ authproof verify --receipt 0x7f3a... [1] Receipt signature PASS [2] Revocation check PASS [3] Time window PASS [4] Scope validation PASS [5] Operator instruction hashPASS [6] Program hash PASS [7] Session risk evaluationPASS [8] Tool schema integrity PASS [9] Model state attestationPASS [10] Tool output hash bindingPASS [11] Instruction provenancePASS [14] Parent scope containment SKIP (root receipt) [15] Authority state drift PASS ✓ Authorization verified. Receipt pre-dates execution. Delegation Receipt → signed by user Model Commitment → bound to receipt Execution Proof → software-attested measurement Action Log → tamper evident chain Delegation Chain → scope attenuation enforced [session] trust: 97.3 | risk: 12.1 | ALLOW

// by the numbers
1,392
JS tests passing
36
Python tests passing
23
JS test suites
0
Failures
13
Verification checks
2
Core primitives
2
Language SDKs

See it in action

Three scenarios. Watch the decision happen in real time.

 
// Click a scenario above to begin

Minimal integration surface.

One client. One receipt. Every subsequent action is locked to it.

agent.js
import { AuthProofClient, ScopeSchema } from 'authproof'

const receipt = await client.delegate({
  scope: new ScopeSchema({
    allowedActions: [{ operation: 'read',   resource: 'email' }],
    deniedActions:  [{ operation: 'delete', resource: '*'     }]
  }),
  operatorInstructions: 'Summarize inbox only',
  expiresIn: '2h'
})

// Actions routed through the gate cannot exceed this receipt
// The signed receipt wins over operator log metadata
// Model substitution is detectable with model-state attestation wired in

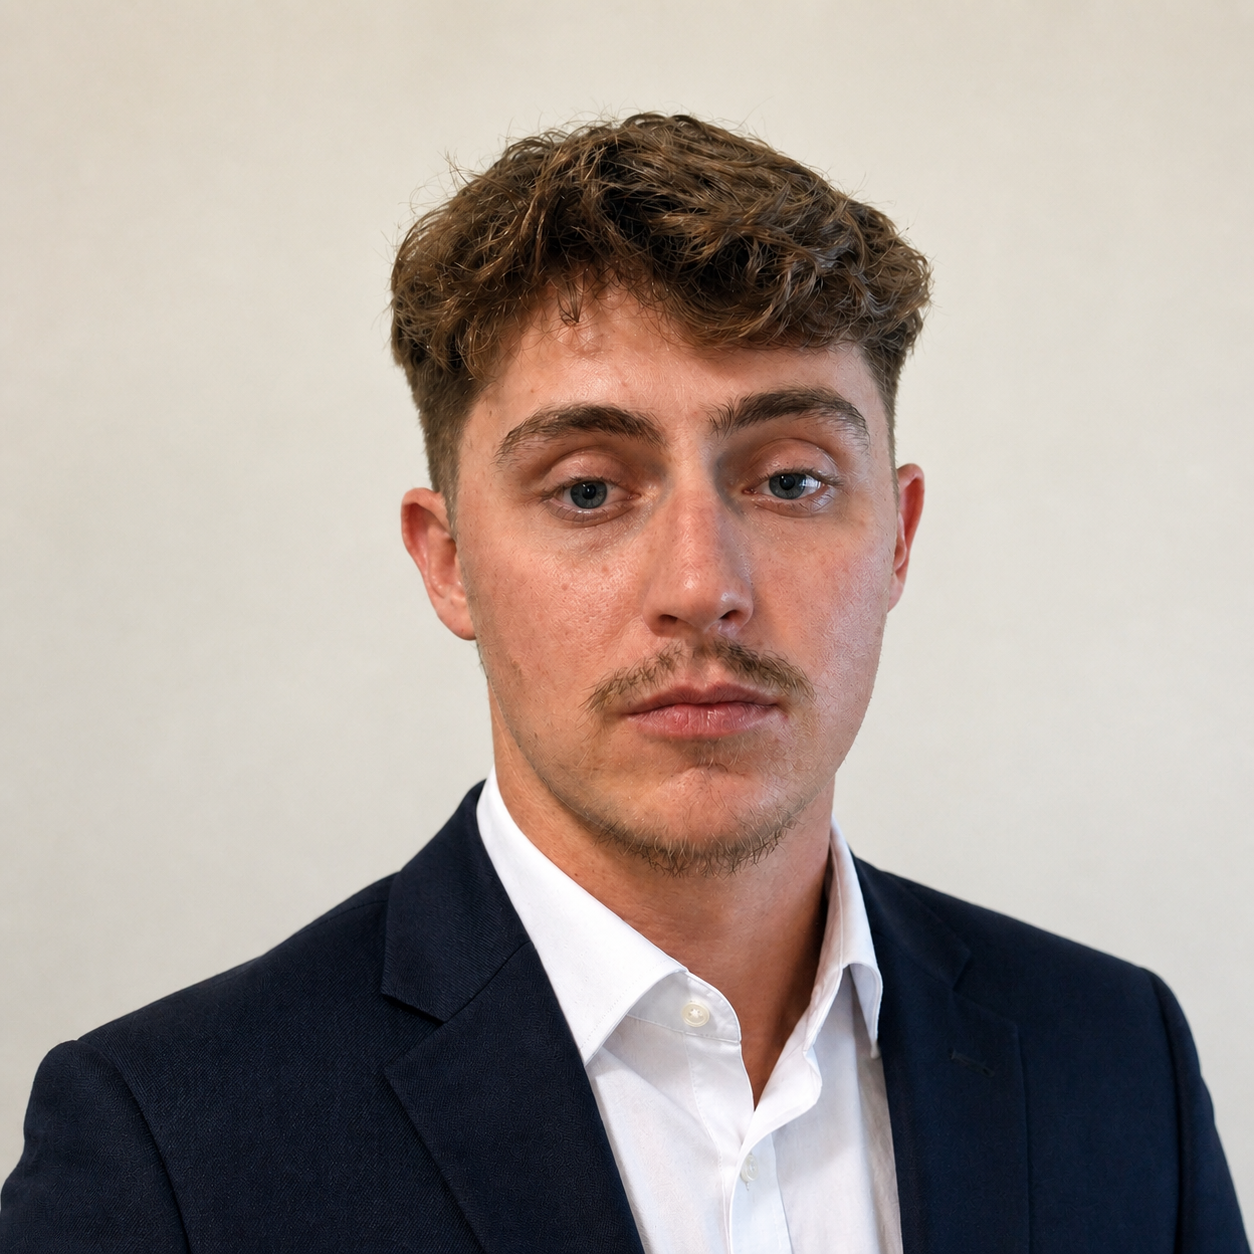
Ryan Nelson

Built by one person

I am Ryan Nelson. HVAC technician at Arctic Air. Accounting student at Oklahoma State University. Father of a daughter turning three in June.

I spent the last month building Authproof because the PocketOS incident showed what happens when AI agents act without cryptographic proof of what they were authorized to do. Nobody else was solving this at the protocol layer.

IETF Internet-Draft filed April 2026. 1,392 JS tests + 36 Python tests, all green. MIT licensed.

Full time job. Full time school. Built it anyway.